

Archive
Software Composition
-
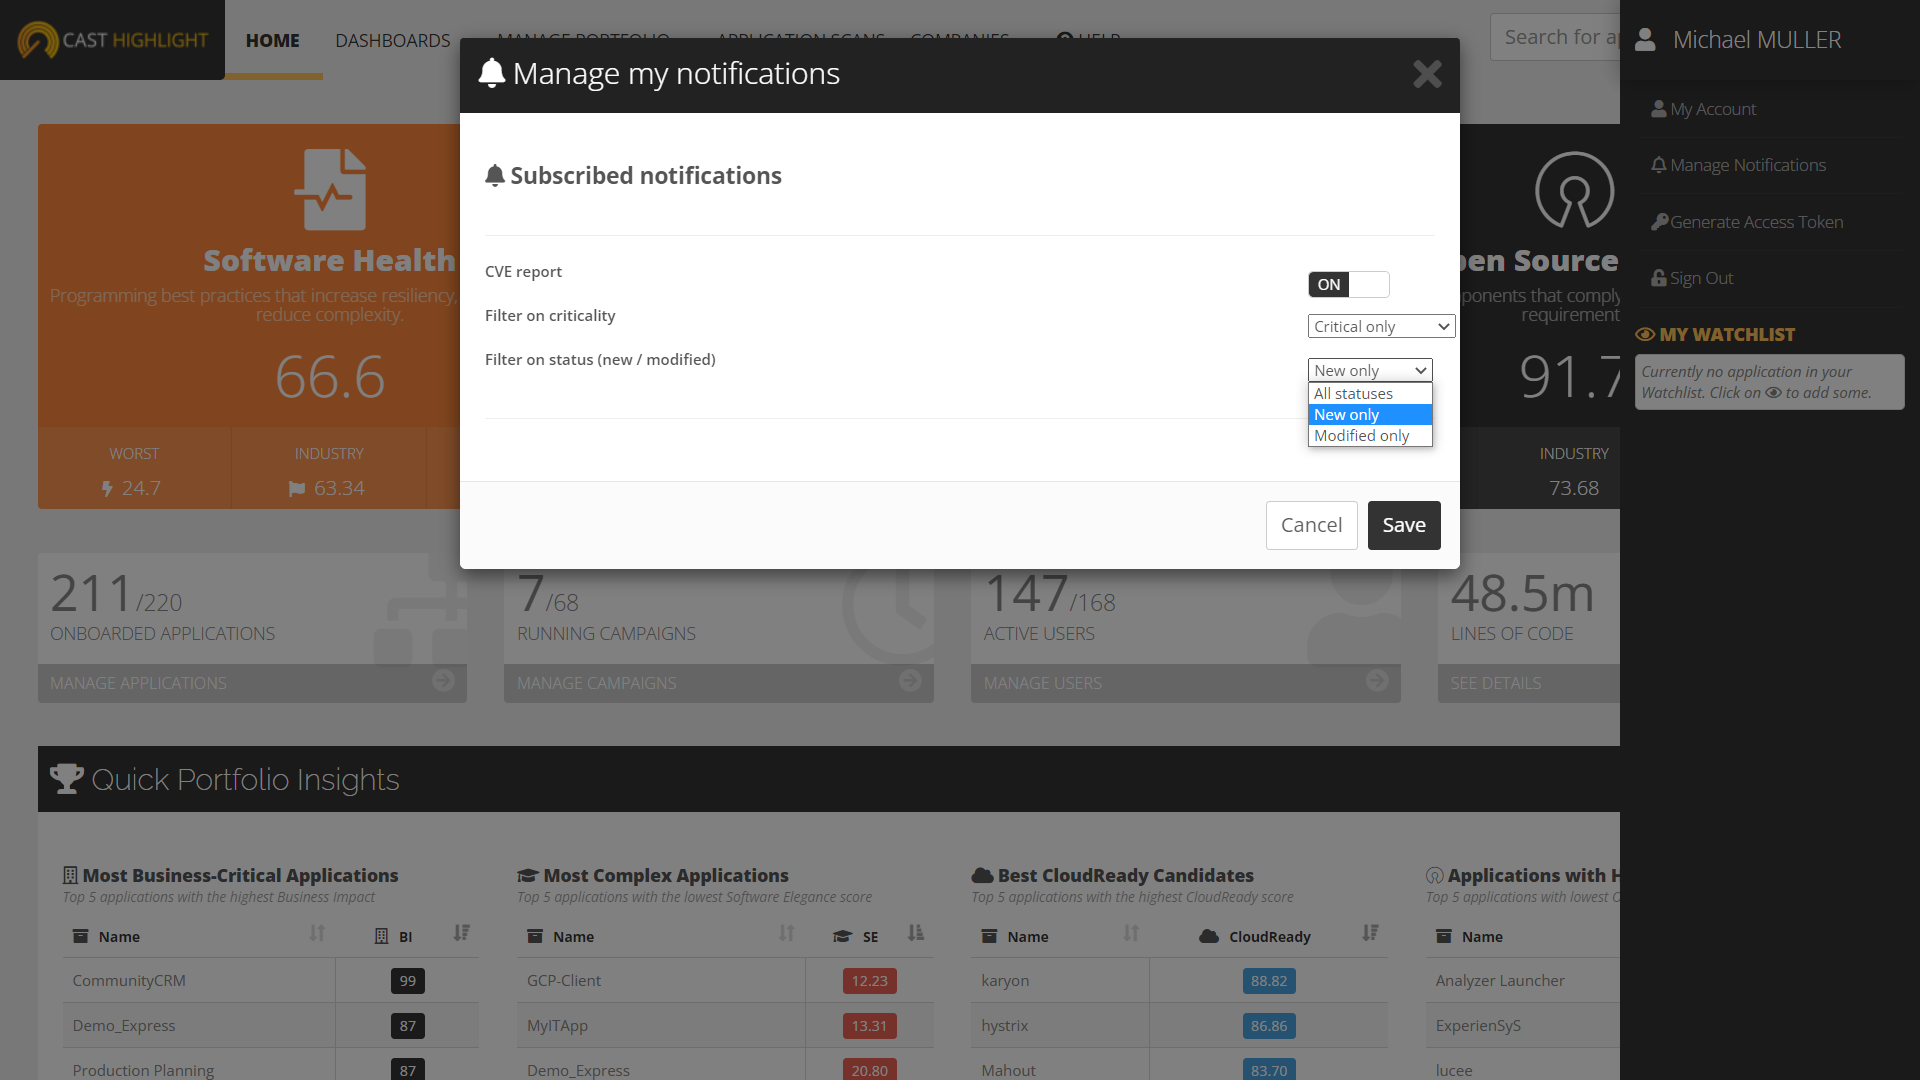
Feature Focus: Automated Email Notifications of New Component Vulnerabilities
The recent security vulnerabilities reported in the Log4J and Spring4Shell open source components reminded us of an important reality — security is often a…
-

Feature Focus: How to automatically generate a License Risk Profile based on the CAST Highlight license rulebook
In CAST Highlight, you can manually or automatically create custom License Risk profiles that will specify the level of risk of licenses detected in…
-

Feature Focus: Open Source License Rulebooks
CAST Highlight now displays open source licenses terms, permissions, and constraints in a user-friendly manner: the license rulebooks. This article explains how to access…
-

How to install and use CAST Highlight SCA browser extension
Get Open Source component information (vulnerabilities, license risk, allow/deny status, available versions, etc.) directly in Chromium-based browsers when visiting repository pages on npmjs, nuget,…
-
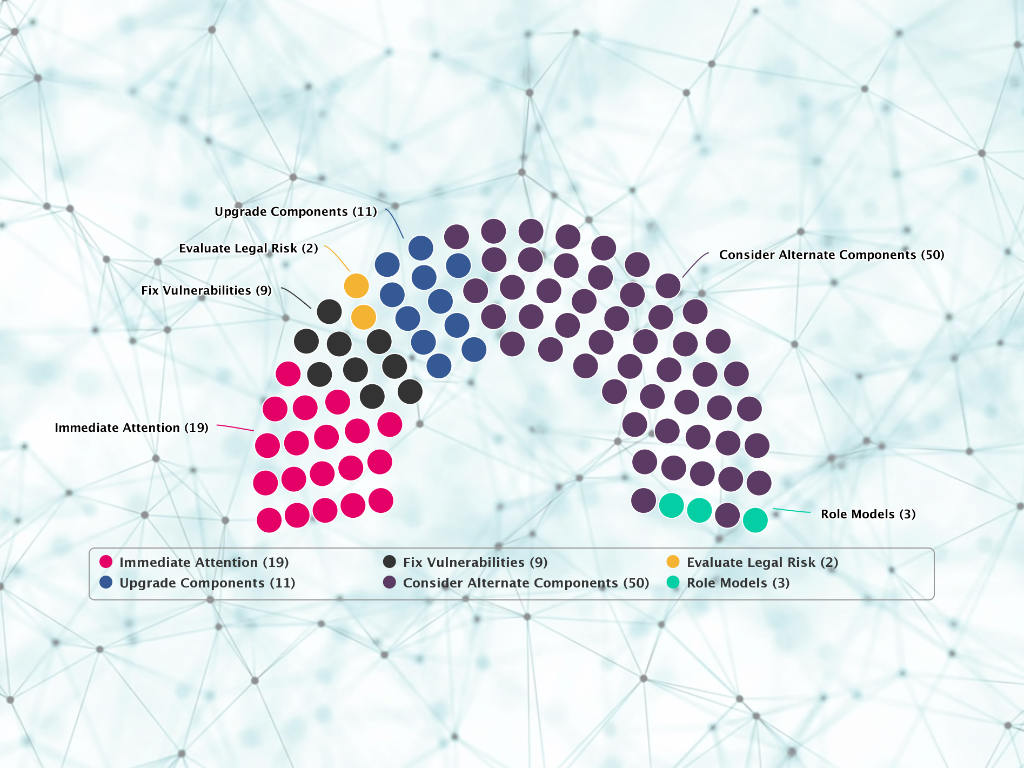
Feature Focus: Portfolio Advisor for Open Source, an automated and smart way to segment an application portfolio better prioritizing third-party component risks
We are very proud to present the Portfolio Advisor for Open Source which joins the growing family of Portfolio Advisors that have already been…
-

Analyze Open Source weaknesses before they become known vulnerabilities with CAST Highlight’s OSSIDB
While it is important to ensure that your application is not exposed to known vulnerabilities from the National Vulnerability Database (NVD), a hacker could…
-
Feature Focus: How to manage third-party components and vulnerabilities in SCA results
CAST Highlight recently introduced new Software Composition Analysis (SCA) features that help users better manage, filter and tag detected Open Source components and related…
-

Feature Focus: Preventing the Use of Risky OSS Components Across the Enterprise
CAST Highlight scans your applications and automatically detects the third-party components in use along with consolidated metadata such as vulnerabilities (CVEs), licenses, version release…
-
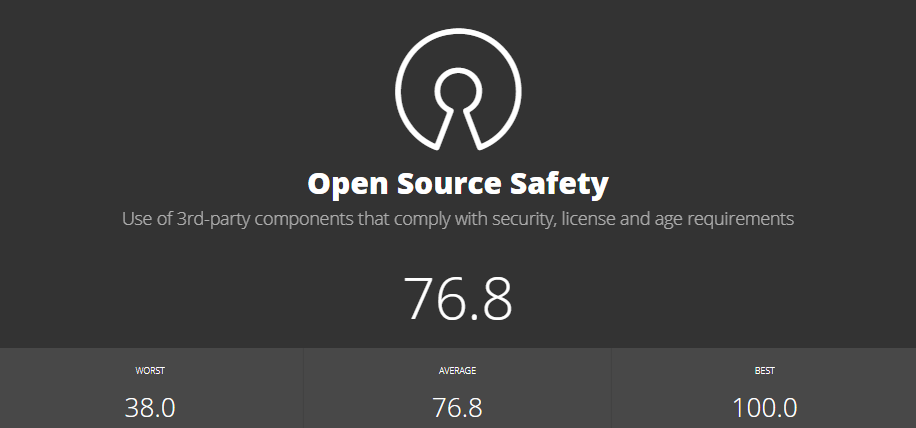
Open Source Safety
Open Source Safety indicates the use of 3rd-party components that comply with security, license and age requirements.
-
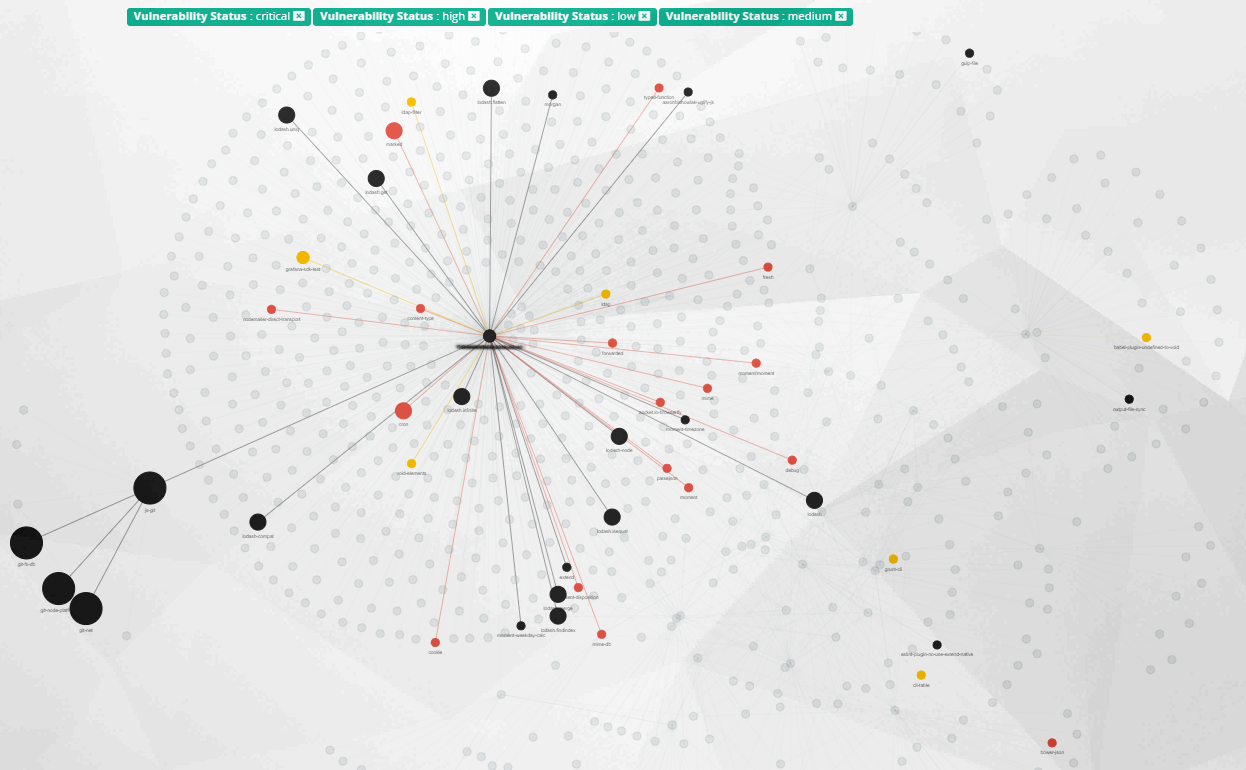
Explore your OSS dependencies. Visually!
Software Composition Analysis is often perceived as a complex discipline, especially when you consider all its aspects such as license compliance, security vulnerability and…